Author, Writer & Editor: MD MOHMMAD ABBAS
Affiliation: THE WORLD’S UPDATE
Date: November 19, 2026
European Commission Targeted in Cyberattack
The European Commission has been targeted in a cyberattack that may have exposed significant amounts of personal data, according to a report published on November 19, 2026.
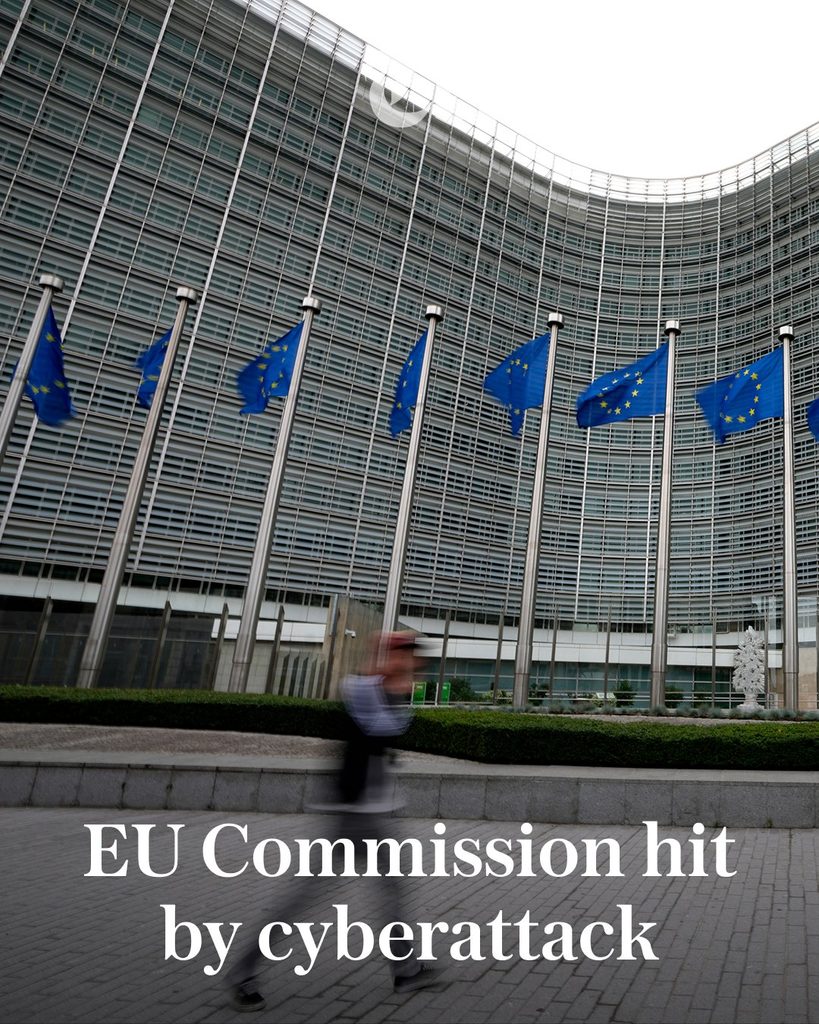
The incident affected individual systems within the European Union’s executive institution. The full extent of the potential damage remains unclear, and investigations are ongoing.
Reuters reported the incident, citing a POLITICO report and information from an EU official.
Employee Services Disrupted
The cyber incident reportedly disrupted services for approximately 10 days.
Among the affected systems were:
- Human resources services used for payslips and time management.
- Systems handling medical expense reimbursements.
These services are used for internal employee administration, making the potential exposure of personal information a significant concern.
European Commission Confirms Cyber Campaign
European Commission spokesperson Thomas Regnier confirmed that the institution had taken action in response to a detected cyber campaign.
He stated that individual systems had been targeted and that people concerned had been informed in accordance with the Commission’s standard procedures.
The Commission reportedly believes that most of the attack has been contained. However, the complete extent of any data exposure has not yet been established.
Senior Officials Briefed on the Incident
According to the reporting, the Commission convened its highest-level internal crisis management body for an urgent meeting concerning the cyber incidents.
Technology Commissioner Henna Virkkunen also briefed fellow commissioners on the situation.
The response includes security measures and efforts to restore affected services.
Who Is Responsible?
As of November 19, the publicly available reporting cited here does not establish who carried out the cyberattack.
No specific country, hacking group or state actor should be identified as responsible without verified evidence.
The Bottom Line
The incident raises important questions about cybersecurity within European institutions and the protection of sensitive employee information.
While the European Commission says it has taken steps to contain the attack, the full extent of the potential data exposure remains unknown.
The investigation will be important in determining what information was accessed, whether data was stolen and who was responsible.
Sources:
- Reuters — EU Commission targeted in cyberattack, November 19, 2026
- Reuters report reproduced by Euronext
THE WORLD’S UPDATE
Standing with the oppressed. Speaking for the unheard. Seeking truth without fear.