A history of major cryptocurrency thefts reveals recurring weaknesses in exchanges, digital wallets, private-key management and transaction approval systems. Despite years of security upgrades, billions of dollars continue to disappear. The central question is no longer just how hackers are breaking in, but why the industry has repeatedly failed to prevent these attacks.
The cryptocurrency industry has spent years presenting blockchain technology as a secure alternative to traditional financial systems. Yet a long series of major cyberattacks has raised a fundamental question about that promise: if digital assets are protected by advanced cryptography, why do exchanges and crypto platforms continue to lose billions of dollars?
The answer lies in an important distinction. In many major incidents, attackers did not break the underlying blockchain. They compromised the systems surrounding it — exchanges, online wallets, private keys, employee devices, transaction-signing processes, smart contracts and cross-chain bridges.
These are not isolated technical problems. Together, they expose a continuing challenge for the industry’s security architecture and its responsibility towards customers.
A history of major cryptocurrency thefts
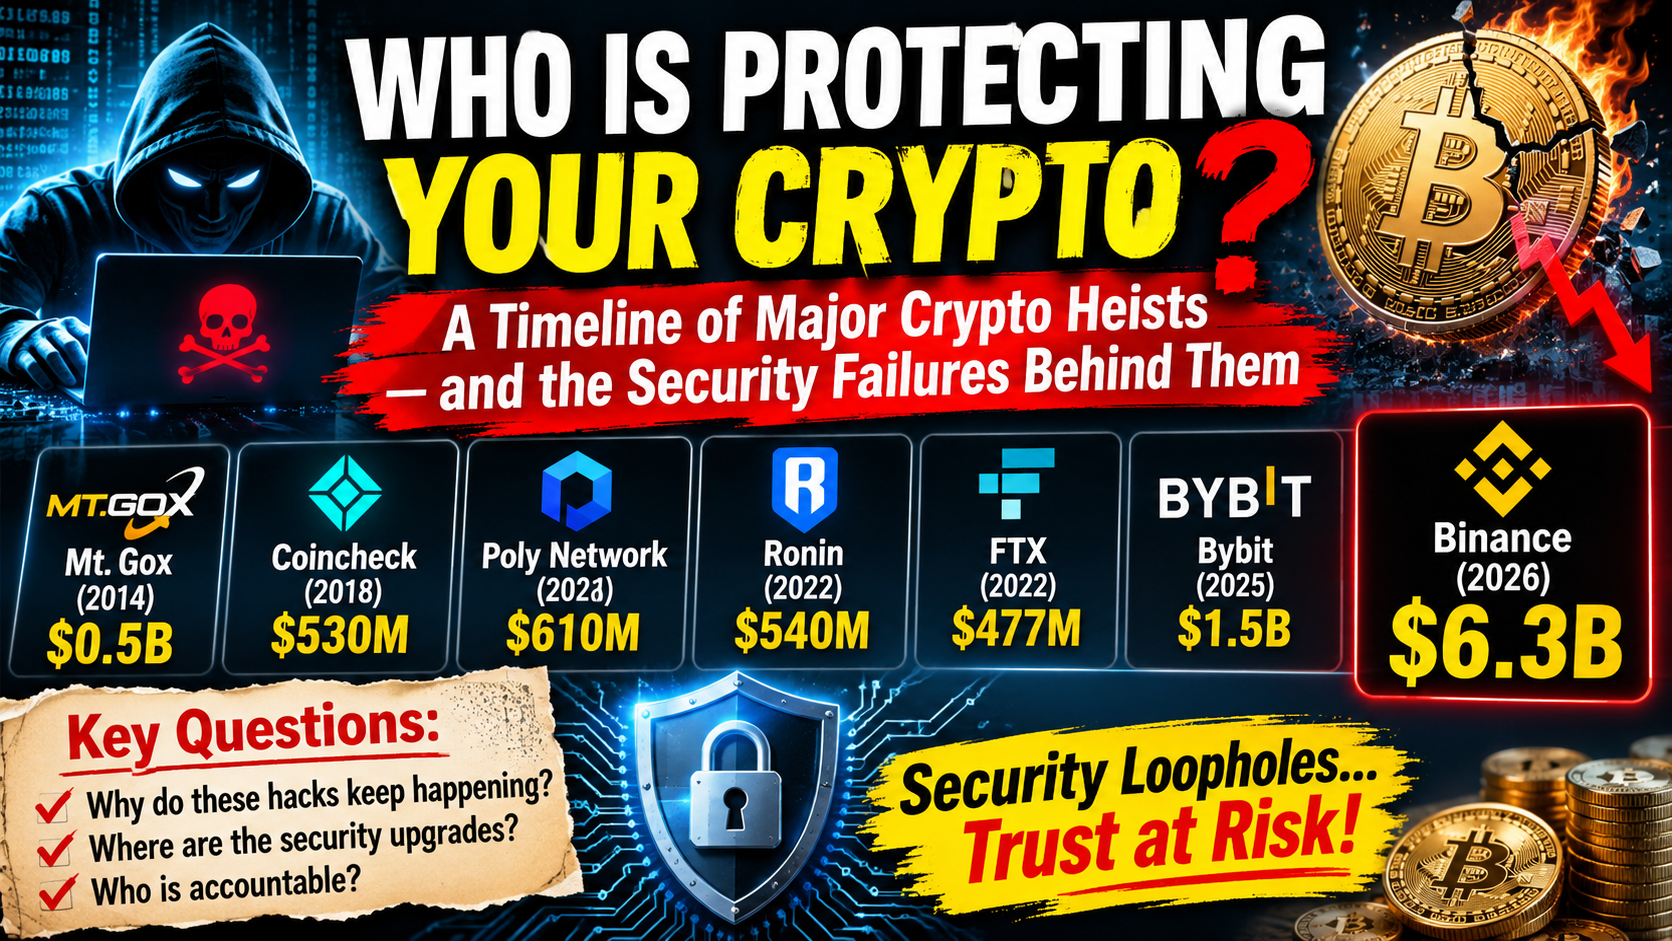
1. Mt. Gox — 2011–2014: Nearly 850,000 Bitcoin reported missing
One of the earliest and most consequential cryptocurrency failures involved Tokyo-based Mt. Gox, which once handled a major share of global Bitcoin trading.
Approximately 850,000 BTC were reported missing, with the value at the time estimated at close to $500 million. The exchange entered bankruptcy proceedings in 2014, leaving around 24,000 customers affected.
The incident exposed serious weaknesses in exchange accounting, operational controls and wallet security. It became an early warning that owning cryptocurrency and safely holding cryptocurrency on an exchange were two different things.
2. Coincheck — January 2018: Approximately $530 million stolen
Japanese exchange Coincheck lost NEM cryptocurrency worth approximately $530 million after attackers compromised an online hot wallet.
The incident raised questions about the exchange’s reliance on internet-connected wallet storage and the absence of stronger cold-storage arrangements.
Coincheck subsequently announced customer compensation and strengthened its security arrangements. However, the incident demonstrated that holding large customer balances in accessible online wallets can create a significant concentration of risk.
3. KuCoin — September 2020: Approximately $281 million stolen
KuCoin suffered a major security breach involving private keys associated with its hot wallets. Multiple digital assets were affected.
The incident showed that even when exchanges operate across several blockchains, a compromise of privileged wallet credentials can create risks across multiple assets.
The company worked with blockchain projects and industry partners to freeze or recover some of the affected assets. The case also highlighted the importance of secure private-key storage and coordinated incident response.
4. Poly Network — August 2021: Approximately $610 million exploited
The Poly Network attack exposed weaknesses in cross-chain transaction infrastructure.
Attackers exploited a vulnerability in the system’s smart-contract permissions and transferred assets worth approximately $610 million.
In an unusual development, the attacker later returned nearly all the funds.
The incident nevertheless demonstrated that smart-contract audits and access-control protections are essential. A vulnerability in the logic governing asset transfers can put enormous sums at risk.
5. Ronin Network — March 2022: Approximately $540 million stolen
The Ronin Network, associated with the Axie Infinity gaming ecosystem, suffered a major breach involving compromised validator keys.
Attackers stole approximately 173,600 ETH and 25.5 million USDC, worth around $540 million at the time.
The incident highlighted a critical weakness in systems that depend on a limited number of validators or signing authorities. If enough trusted keys are compromised, attackers may be able to authorise transactions that appear legitimate to the network.
6. FTX — November 2022: Approximately $477 million in unauthorised transfers reported
During the collapse and bankruptcy of cryptocurrency exchange FTX, approximately $477 million in cryptocurrency was reported to have been transferred without authorisation.
The incident raised serious questions about asset custody, internal controls and the separation of customer funds from company operations.
It is important to distinguish this event from a conventional external exchange hack: the transfers occurred amid the company’s bankruptcy crisis, and the full circumstances and accounting of the assets were complex.
7. DMM Bitcoin — May 2024: Approximately $305 million stolen
Japanese exchange DMM Bitcoin lost 4,502.9 BTC, valued at more than $300 million at the time.
The incident was associated with a compromise of the exchange’s Bitcoin custody arrangements. The exact technical sequence was not fully established in the initial reporting.
DMM arranged to cover customer balances through group-company support and later transferred customer accounts and custodial assets to SBI VC Trade.
This distinction matters: reimbursing customers from company funds is not the same as recovering the stolen Bitcoin.
8. Bybit — February 2025: Approximately $1.5 billion stolen
The Bybit breach became one of the largest cryptocurrency thefts ever recorded before the 2026 Binance incident.
Approximately $1.5 billion in digital assets was taken from wallets connected to the exchange.
The attack involved a compromised transaction-signing process. The attackers manipulated what authorised signers saw during transaction approval, causing a transaction to be approved under misleading circumstances.
The FBI attributed the attack to North Korea-linked TraderTraitor activity. Bybit suspended withdrawals, investigated the breach and worked to rebuild its wallet security arrangements.
The incident exposed a critical weakness: multiple signatures do not guarantee safety if the people signing a transaction cannot independently verify what they are actually authorising.
9. Binance — October 2026: Approximately $6.3 billion in reported stolen assets
The latest incident has brought the security debate to an unprecedented scale.
Binance reported that attackers compromised its hot-wallet infrastructure on October 29, 2026, resulting in the loss of approximately $6.3 billion in token assets.
Its initial investigation suggested that a compromised DevOps engineer’s laptop may have enabled access to a service container from which unauthorised withdrawal transactions were submitted. Binance later disclosed that investigators had identified additional breach points.
The company said it had found no evidence that wallet private keys were leaked. It also reported working with law-enforcement agencies, blockchain intelligence firms and industry partners to freeze affected assets.
Binance said approximately $3 billion had been frozen on-chain and committed to covering customer losses through its SAFU fund and corporate resources.
On October 31, Binance said it had replenished approximately 90% of the affected assets. Its November 1 recovery update said the figure had reached approximately 95%, with withdrawals being restored in phases after security checks.
These are important recovery measures, but they do not answer the central question: how did the security architecture permit such a large unauthorised withdrawal in the first place?
What do these incidents reveal about crypto security?
The pattern across these cases is significant. The attack methods differ, but several weaknesses appear repeatedly.
1. Hot-wallet concentration: Large amounts of customer assets remain exposed to internet-connected systems. If access controls fail, the potential loss can be enormous.
2. Private-key and signing vulnerabilities: A private key or signing authority can effectively control valuable assets. Poorly isolated keys and weak approval processes can undermine otherwise sophisticated security systems.
3. Employee and developer access: An employee’s laptop, developer credentials or internal service can become an entry point into critical infrastructure. Access to production systems must be tightly restricted and continuously monitored.
4. Multi-signature weaknesses: Multiple approvals are not enough if signers receive misleading transaction information or use compromised interfaces. Independent verification is essential.
5. Smart-contract and bridge vulnerabilities: Poorly designed permissions, validator systems and cross-chain bridges can allow attackers to move assets without the intended authorisation.
6. Delayed detection and response: Monitoring systems must identify abnormal withdrawals quickly, enforce transaction limits and activate emergency controls before large-scale losses occur.
7. Weak transparency and accountability: Customers often learn about the technical failure only after assets have disappeared. Independent investigations and detailed public post-incident reports are necessary to establish what failed and why.
The numbers show that the problem is structural
TRM Labs’ January 2026 Crypto Crime Report estimated that approximately $2.87 billion was stolen across nearly 150 crypto hacks and exploits during 2025.
Of that amount, infrastructure attacks accounted for approximately $2.2 billion, or 76% of the total. These included compromises involving private keys, wallet infrastructure, privileged access and other operational systems.
The report also identified the February 2025 Bybit breach as a defining incident, accounting for approximately $1.46 billion in losses.
This is an important finding. It suggests that the biggest financial risks are not limited to flaws in blockchain code. Security weaknesses in the organisations and infrastructure managing digital assets can be equally, if not more, consequential.
What changed after the attacks — and what remains unresolved?
The industry has introduced or expanded several security measures over the years:
- Cold storage for large reserves.
- Multi-signature and hardware-backed key management.
- Independent security audits and penetration testing.
- Withdrawal monitoring, transaction limits and emergency pauses.
- Bug-bounty programmes and external vulnerability reporting.
- Blockchain monitoring and cooperation with law enforcement.
- Proof-of-Reserves reporting and customer compensation arrangements.
But these measures have limitations.
Proof of Reserves can help users examine whether an exchange holds assets corresponding to reported customer balances. It does not, by itself, prove that the exchange’s internal systems cannot be compromised or that every liability has been disclosed.
Likewise, a security audit conducted before an attack cannot guarantee that employee devices, privileged credentials or transaction-signing interfaces will remain secure.
The repeated incidents suggest that security must be treated as a continuous operational responsibility rather than a one-time compliance exercise.
Binance’s recovery is not the same as a security solution
Binance’s decision to cover the reported losses, freeze affected assets and restore withdrawals in phases addresses the immediate financial and operational crisis.
However, customer reimbursement and security reform are two separate responsibilities.
A company can replace stolen assets, but that does not automatically establish that its security architecture is safe against another attack.
The decisive test will be the independent technical findings, the full incident post-mortem and whether the company implements safeguards that prevent a similar breach.
The same standard should apply to every major exchange and digital-asset custodian.
Who is accountable when customers’ money is stolen?
The criminal responsibility belongs to the attackers. But that does not eliminate the responsibility of the institutions entrusted with protecting customer assets.
If a bank repeatedly suffers major thefts, the public would reasonably demand answers about its security systems, management decisions, internal controls and regulatory oversight.
Crypto exchanges should face the same questions.
- Why were critical systems vulnerable?
- Were known weaknesses identified before the attack?
- Were security recommendations implemented?
- Could abnormal withdrawals have been stopped earlier?
- Were customer assets adequately separated from operational infrastructure?
- Who independently verifies that promised security upgrades have actually been completed?
These are not questions that can be answered simply by identifying the hacker or announcing a compensation package.
The real issue: Trust cannot depend on promises
Cryptocurrency technology may offer new ways to transfer, store and manage digital assets. But the public does not interact only with blockchain code. Millions of users depend on exchanges, wallet providers, custodians and other intermediaries to safeguard their money.
Every major breach weakens confidence in that relationship.
The industry’s future will depend not only on faster transactions, new tokens or larger trading volumes, but also on whether companies can demonstrate that customer assets are protected by independently tested security systems.
The central question remains: When hackers repeatedly find ways into crypto platforms, who is responsible for ensuring that the same security failures do not happen again?
A criminal must be held accountable for stealing. But the institutions entrusted with protecting people’s money must also explain how the theft became possible — and prove that the weaknesses have been fixed.
The issue is not simply how much cryptocurrency has been stolen. It is why, after years of major breaches and repeated promises of stronger protection, the same fundamental security failures continue to threaten public trust
SOURCE :
Reuters — Crypto’s biggest hacks and heists: Historical incidents and reported losses. Read Reuters’ report.
Reuters — Binance $6.3 billion breach factbox: Comparison with major historical incidents. Read the factbox.
OECD — Asia Capital Markets Report 2026: Exchange security incidents, including Mt. Gox, Coincheck and KuCoin. Read the OECD report.
The Block — Bybit and 2025 crypto hacks: Technical analysis of wallet and signing-system vulnerabilities. Read the analysis.
Binance official security updates: Initial incident statement · October 30 investigation update · November 1 withdrawal recovery update.
Leave a Reply